
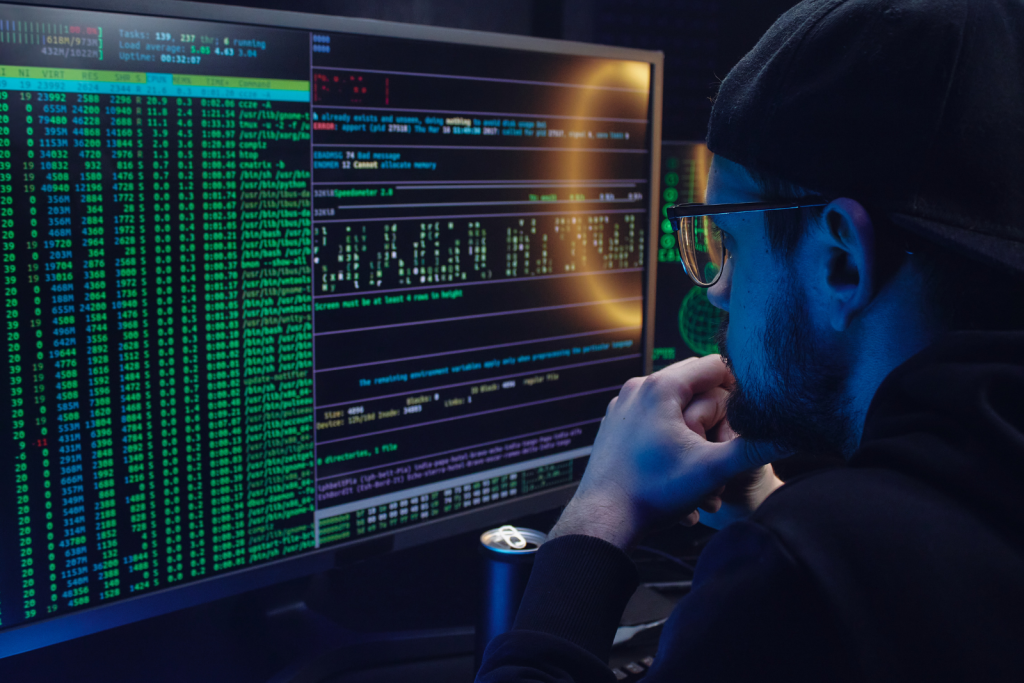
Penetration tester at a terminal running a live assessment
Penetration Testing

Find Out How You'd Actually Get Breached — Before Someone Else Does

We put certified ethical hackers against your network, applications, and cloud the same way a real attacker would,
then hand you a plain-language report that shows exactly what we got into, how we got there, and what to fix first.

OSCP-Certified Testers · CMMC Level 2 · SOC 2 Type II · ISO/IEC 27001 · Denver, CO & Washington, D.C.
100%
Human-led testing, not automated scans repackaged as a report
48hr
Preliminary findings shared before your final report arrives
10+
Active security certifications held across our testing team
241 days
Average time to detect and contain a breachIndustry avg. — IBM
92%
Of breaches trace back to flaws in the organization's own systemsIndustry avg. — IBM
The Case for Testing

Your defenses look solid. That's not the same as being solid.

Most organizations find out they have a gap the hard way — after an incident.
A penetration test lets you find those gaps first, on your schedule, without a real attacker on the other end.

Real Attacks, Not Just Scans

Automated scanners flag known issues and stop there. Our testers chain weaknesses together the way an actual attacker would, uncovering the gaps scanners miss entirely — so you see what can really happen, not just what might.

Reports Your Auditors Will Accept

PCI DSS, HIPAA, SOC 2, CMMC, and FedRAMP all require third-party penetration testing. Our reports are built to satisfy auditors directly, not just give you something to translate for them.

A Fix List You Can Actually Act On

Every finding is prioritized by real-world risk, not CVSS score alone. You'll know what to fix first, why it matters, and how — and we stay available through your entire remediation cycle.

What We Test

Choose the test that fits your exposure

Each engagement is scoped to your environment. Not sure which type you need?
Tell us what you're worried about and we'll point you in the right direction.

External

External Network Penetration Test

We attack what anyone with an internet connection can see.

  • Reconnaissance of your public-facing systems and footprint
  • Firewall, router, and web server attack simulation
  • Exploitation of exposed services and misconfigurations
  • Credential attack testing against public-facing login portals
  • Testing whether initial access leads deeper into your environment

Good fit for: Any organization with internet-facing systems, remote access tools, or customer-facing portals.

Internal

Internal Network Penetration Test

We simulate what happens after someone's already inside.

  • Tests your defenses assuming an attacker has initial access
  • Lateral movement and privilege escalation across your network
  • Active Directory and identity system attack paths
  • Endpoint and access control validation
  • Network segmentation bypass and data exfiltration simulation

Good fit for: Organizations validating internal defenses, zero-trust controls, or CMMC requirements.

Web App

Web Application Penetration Test

We look for vulnerabilities in the apps your users and customers rely on.

  • Full OWASP Top 10 coverage
  • SQL injection, cross-site scripting, and authentication bypass
  • Session management and token security analysis
  • Business logic flaw testing specific to how your app works
  • API and third-party integration security

Good fit for: Any organization whose product, portal, or internal tools are built as a web application.

Cloud & Network

Cloud & Full Network Assessment

Your perimeter is everywhere now — we test it that way.

  • AWS, Azure, and GCP configuration review and attack simulation
  • IAM policy review and privilege abuse testing
  • Wireless access point security testing
  • On-premises to cloud attack path mapping
  • Data storage and backup security validation

Good fit for: Hybrid environments and organizations with workloads moving to, or already in, the cloud.

How It Works

From kickoff to clean report in 2–3 weeks

No surprises. Here's exactly what happens after you reach out.

1

Scoping Call

We define what's in scope, rules of engagement, and your timeline. You decide what we test. 1–2 days

2

Reconnaissance

We gather intelligence on your environment the same way a real attacker would, before touching anything. 2–5 days

3

Active Testing

Our team attacks your systems using real attacker tools and techniques within agreed rules. 5–10 days

4

Analysis & Report

Every finding is validated, risk-ranked, and written up with step-by-step remediation guidance. 3–5 days

5

Debrief & Support

We walk your team through findings live, and stay available while you fix things. Ongoing

What You Receive

Reports your team and your auditors can both use

Every engagement produces documentation written for two audiences:
your technical team who needs to fix things, and your leadership or auditors who need the big picture.

Executive Summary

A plain-language overview of your overall security posture and top priorities, written for leadership, not security engineers.

Technical Findings Report

Every vulnerability documented with severity rating, how we reproduced it, evidence screenshots, and specific remediation steps.

Attack Timeline

A chronological walkthrough showing exactly how our testers moved through your environment, so your defenders understand what happened and when.

Prioritized Fix List

Findings organized by risk level with effort estimates and sequencing guidance, so your team knows where to start.

Live Debrief Session

A walkthrough call with the actual testers who worked your engagement, not a sales rep, so your team can ask detailed follow-up questions.

Retest Support

After you've remediated, we confirm the fixes actually worked — included for critical findings, available for all findings on request.

Certifications

Held by our organization and our testing team

Company-level certifications shown below; see the full list and audit history on the Certifications page.

CMMC Level 2

Confidential Unclassified Information handling

ISO logo

ISO/IEC 27001

Information security management system

SOC 2 Type II

Independently audited security controls

NIST logo

NIST SP 800-171

Controlled unclassified information protection

OSCP CEH CRTP CISSP GCIH GCFA CySA+ CISA CISM CRISC PCNSA

CMMC and SOC 2 seals shown are custom-designed here (no verified right to display the official trademarked badge); ISO and NIST marks are the real, freely-licensed logos.

Don't Wait for an Incident

Know where you're vulnerable, before someone else does

The average U.S. data breach now costs $10.2 million and takes 241 days to detect (IBM, 2025). A penetration
test costs a fraction of that, and gives you the information you need to close gaps before attackers find them.

Book a Free Call