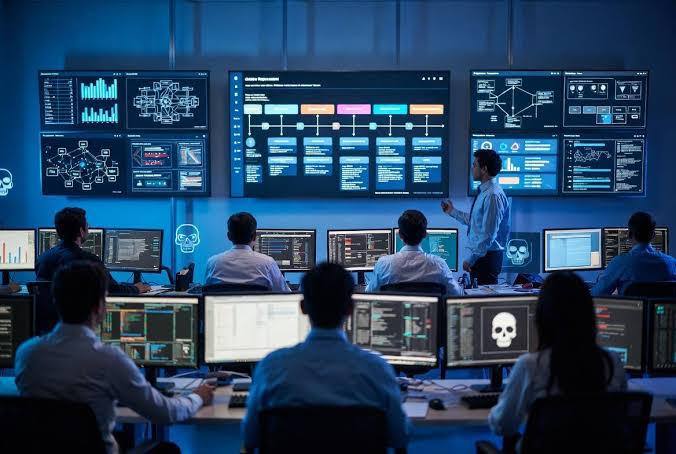
Incident response team monitoring dashboards in a security operations center
Incident Response and Recovery

When You're Breached, Every Minute Makes It Worse

We detect, contain, and recover from cyber incidents fast, limiting the business disruption, data loss, and compliance fallout that follow a slow response.
From the moment you call, our team leads containment, eradication, and recovery, then hands you a clear report of what happened and how we fixed it.

CMMC Level 2 · SOC 2 Type II · ISO/IEC 27001 · Denver, CO & Washington, D.C.
Why Response Speed Matters

The gap between breach and response is where the damage happens

The longer a threat sits undetected and uncontained, the more it costs you in downtime, data, and trust.
A fast, structured response is what determines whether an incident becomes a footnote or a crisis.

Slow Response Sinks Businesses

Industry research shows 60% of small businesses that suffer a breach close within six months of the incident. How fast and how well you respond in the first hours often decides which side of that number you land on.

Detection Tools Alone Aren't Response

Advanced detection and remediation tools using AI and machine learning help identify and categorize threats faster than ever, but the technology is only half the equation. It takes experienced responders to act on what they find.

Compliance and Evidence Don't Wait

A well-run incident response preserves the evidence you need for investigators and insurers, and keeps you positioned to meet the compliance requirements that follow any reportable incident.

What's Included

Response capabilities built for the moment you need them

Every engagement is backed by the same core toolkit and team, ready before you ever have to call.

Swift Response

Our experts are on standby to respond to a security incident the moment it's confirmed, not after a wait in a support queue.

Advanced Detection & Analysis Tools

We bring industry-leading tools that use machine learning and other advanced techniques to speed up detection and analysis throughout the response process.

Detailed and Specific Incident Reports

You'll see exactly how the incident occurred, which vulnerabilities were used, and what steps were taken to prevent it from happening again.

End-to-End Support

From initial detection through post-incident analysis and recommendations, we handle the full incident response lifecycle, not just the parts that are easy.

24/7 Emergency Response

One call sets every stage of recovery in motion

Whatever time you call, the same proven process starts immediately — from first triage to the final report.

Step 1

Prepare

Triage playbooks and readiness checks, run before you ever need them.

Step 2

Identify & Analyze

Scope the incident and run forensic analysis to see what's really happening.

Step 3

Contain

Isolate compromised systems before the incident can spread any further.

Step 4

Eradicate

Remove the malicious presence completely, not just the visible symptoms.

Step 5

Recover & Restore

Bring services back online and confirm everything works as it should.

Step 6

Post-Incident Activity

Review what happened and strengthen your defenses against a repeat.

Our Incident Response Process

A structured process from first alert to final report

No guesswork, no wasted motion. Here's what happens once you bring us in.

1

Detection and Identification

24/7 monitoring identifies threats in your environment in real time.

2

Containment

We act fast to contain the breach where it stands, preventing intruders from spreading further.

3

Eradication & Remediation

We remove the threat and apply patches and other security measures to prevent it from recurring.

4

Recovery

We restore normal business operations with minimal disruption.

5

Post-Incident Analysis & Reporting

We deliver a thorough report detailing the incident, the vulnerabilities used, the patches applied, and steps to keep you safe going forward.

Certifications

Certifications behind every incident response engagement

Company-level certifications shown below; see the full list and audit history on the Certifications page.

CMMC Level 2

Confidential Unclassified Information handling

ISO logo

ISO/IEC 27001

Information security management system

SOC 2 Type II

Independently audited security controls

NIST logo

NIST SP 800-171

Controlled unclassified information protection

OSCP CEH CRTP CISSP GCIH GCFA CySA+ CISA CISM CRISC PCNSA

CMMC and SOC 2 seals shown are custom-designed here (no verified right to display the official trademarked badge); ISO and NIST marks are the real, freely-licensed logos.

Don't Wait for the Call You Hope Never Comes

Have a response plan in place before you need one

60% of small businesses that experience a breach close within six months of the incident (industry research).
Fast, structured incident response is what stands between a contained event and a business-ending one.

Book a Free Call