
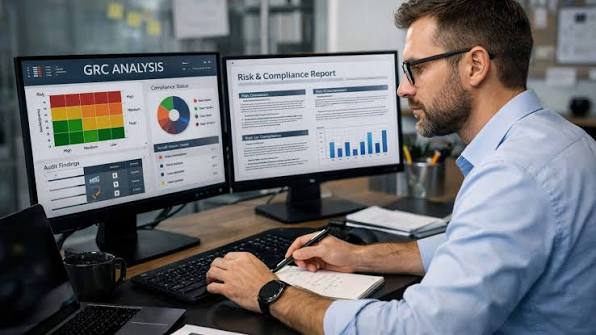
GRC analyst reviewing risk and compliance dashboards
Governance, Risk, and Compliance (GRC)

Stop Guessing Whether You're Actually Compliant

Regulations keep changing, audits keep coming, and cyber risk keeps growing.
Cyberix GRC services give you a clear, structured program, so you always know where you stand and exactly what to do next.

CMMC Level 2 · ISO/IEC 27001 & 31000 · SOC 2 Type II · NIST 800-53 & 800-171 · Denver, CO & Washington, D.C.
7.9/10
Average business risk rating reported by legal & compliance leadersIndustry survey, Q4 2025
60%
Of compliance leaders cite technology risk as their #1 concern todayIndustry survey
$44B
Projected size of the GRC market by 2029, driven by regulatory pressureIndustry projection
$4.4M
Average cost of a data breach in 2025 — GRC programs reduce that exposureIndustry avg.
Understanding GRC

What GRC is, and why it matters to your business

Without a structure connecting your security decisions to your business goals, audits become fire drills and compliance becomes guesswork.
GRC puts a structure around all of it, so you're running a program instead of reacting to one.

Governance

The policies, rules, and decision-making processes your organization uses to operate consistently and ethically. Good governance means everyone knows what the rules are, who's accountable, and how decisions get made, from the executive team down.

Risk Management

Finding, evaluating, and addressing threats before they turn into incidents. This includes cyber threats, third-party vendor risk, regulatory exposure, and operational vulnerabilities, prioritized so your team knows what to tackle first.

Compliance

Meeting the laws, regulations, and industry standards that apply to your business, whether that's CMMC for defense contractors, HIPAA for healthcare, PCI DSS for payment data, or SOC 2 for SaaS companies. GRC makes it systematic, not a scramble.

What We Do

Our GRC services, what's actually included

We tailor every engagement to your size, industry, and regulatory environment.
No generic frameworks pushed onto your team — everything is built for how you actually operate.

Governance

Security Policy & Governance Framework

We build or strengthen the policies, procedures, and oversight structures that define how security is managed across your organization.

  • Security policy development and review
  • Roles, responsibilities, and accountability mapping
  • Cybersecurity metrics and KPI frameworks for leadership
  • Board and executive reporting structures
  • Policy lifecycle management and update processes
Risk

Risk Assessment & Mitigation Planning

We identify where your organization is exposed, across IT, cloud, applications, and third-party vendors, and help you build a plan to address it.

  • Enterprise-wide risk identification and prioritization
  • IT infrastructure and application risk assessment
  • Third-party and vendor risk evaluation
  • Risk quantification and business impact analysis
  • Customized risk mitigation roadmap
Compliance

Regulatory Compliance Programs

We help you get compliant and stay compliant, whether you're working toward CMMC, SOC 2, HIPAA, PCI DSS, or multiple overlapping frameworks.

  • Compliance gap analysis against required frameworks
  • Control design and implementation support
  • Audit preparation and evidence collection
  • Continuous compliance monitoring
  • Policy documentation aligned to audit requirements
Advisory

Cyber Risk Assessments & Advisory

Strategic guidance for leadership teams navigating cybersecurity decisions, investments, and regulatory requirements, without a full internal security team.

  • Executive-level security posture briefings
  • Security investment prioritization guidance
  • Incident response plan review and tabletop exercises
  • Cyber insurance readiness assessment
  • Ongoing virtual CISO advisory (vCISO)
Technology

GRC Technology & Automation

We help you select and implement the right GRC platform for your size and needs, so compliance doesn't rely on spreadsheets and manual tracking.

  • GRC platform evaluation and selection
  • Implementation and configuration support
  • Workflow automation for compliance tasks
  • Dashboard and reporting setup for leadership
  • Ongoing tool support and optimization
Training

Security Awareness & Compliance Training

Your policies only work if your team follows them. We build a culture of security awareness, from executives to frontline staff.

  • Security awareness program design
  • Role-based compliance training
  • Phishing simulation and testing
  • Policy acknowledgment and attestation tracking
  • Training completion reporting for auditors
Frameworks We Work With

We know the regulations that apply to your industry

Whether you're a defense contractor, a healthcare provider, or a growing SaaS company, we build your program around
the frameworks that actually apply to you, not a generic checklist.

CMMC Level 2 NIST SP 800-171 NIST 800-53 ISO/IEC 27001 ISO/IEC 27032 ISO/IEC 31000 SOC 2 Type II HIPAA PCI DSS FedRAMP FISMA CIS Controls GDPR DFARS ITAR
Who This Is For

You need GRC if any of these sound familiar

You Have an Audit Coming Up

We run a gap assessment, get your controls in order, and make sure your documentation is ready before the auditor walks in the door.

You Work With the Federal Government or DOD

CMMC, DFARS, and NIST 800-171 compliance isn't optional for defense contractors. We help you achieve and maintain it without it taking over your operations.

You Handle Sensitive Data

HIPAA, PCI DSS, and state privacy regulations put real legal exposure on organizations that handle health, financial, or personal data. GRC makes sure your controls and documentation hold up.

You're Growing Fast and Security Hasn't Kept Up

New employees, new tools, new vendors — every addition creates risk and compliance surface area. We help you scale your program alongside your business.

Your Security and Compliance Functions Are Siloed

When IT, legal, and operations all manage risk separately, things fall through the cracks. GRC connects them under one coordinated framework.

You Don't Have a Full-Time Security Team

Many mid-sized organizations can't justify a dedicated CISO and compliance staff. Our virtual GRC services give you that expertise without the full-time overhead.

The GRC Framework

Three pillars, working as one coordinated system

Each pillar covers distinct disciplines, but a real GRC program only works when all three move together.

GRC System

Governance

Direction, oversight, accountability

Establishes clear direction, decision rights, and policy across your organization.

  • Policies
  • Processes
  • Oversight
  • Accountability

Risk Management

Identify, assess, reduce exposure

Systematic identification and handling of the risks that could actually hurt your business.

  • Identification
  • Assessment
  • Mitigation
  • Monitoring

Compliance

Meet regulatory & corporate standards

Ensures adherence to the regulations and standards that actually apply to your organization.

  • Regulatory requirements
  • Corporate policy
  • Embedded controls
  • Auditing
How It Works

From discovery to ongoing program, here's what to expect

We start with where you are, not where a generic framework assumes you should be.

1

Discovery & Gap Assessment

We review your current policies, controls, and practices against the frameworks that apply to your business and identify the gaps. Week 1–2

2

Risk Assessment

We map your risk landscape, identifying threats across your network, applications, cloud, and third-party vendors, and rank them by impact. Week 2–4

3

Program Design & Build

We build or strengthen your policies, controls, and documentation, and implement or configure your GRC tooling if needed. Week 4–10

4

Ongoing Management

We monitor your compliance posture, update controls as regulations change, and report regularly to leadership and auditors. Continuous

Why Cyberix

We built our own GRC program. We know what works.

Cyberix holds CMMC Level 2, SOC 2 Type II, ISO/IEC 27001, ISO/IEC 31000, and NIST certifications,
not as a selling point, but because we operate under the same standards we help our clients achieve.

Custom Programs, Not Cookie-Cutter Templates

We don't hand you a generic policy binder. Every policy, control, and procedure we build is designed for how your business actually operates and what your regulators actually require.

Practitioners Who've Been on Both Sides

Our team includes CISMs, CISAs, CRISCs, and CISSPs with real experience both implementing security programs and passing audits. We know what auditors look for because some of us have been auditors.

Compliance That Doesn't Slow You Down

A good GRC program doesn't add bureaucracy — it streamlines how you manage risk and gives your team clarity on what they need to do. We design for usability, not just auditability.

Certifications

We hold what we help you get audited for

Company-level certifications shown below; see the full list and audit history on the Certifications page.

CMMC Level 2

Confidential Unclassified Information handling

ISO logo

ISO/IEC 27001

Information security management system

SOC 2 Type II

Independently audited security controls

NIST logo

NIST SP 800-171

Controlled unclassified information protection

OSCP CEH CRTP CISSP GCIH GCFA CySA+ CISA CISM CRISC PCNSA

CMMC and SOC 2 seals shown are custom-designed here (no verified right to display the official trademarked badge); ISO and NIST marks are the real, freely-licensed logos.

Common Questions

Straight answers about GRC services

What's the difference between GRC consulting and just hiring a compliance officer?

A compliance officer typically manages one area — often just regulatory filing and documentation. GRC consulting gives you a full program: governance structures, risk identification across your whole environment, compliance with multiple frameworks, and ongoing management. For most mid-sized organizations, outsourced GRC delivers more depth and breadth than a single hire can, at a fraction of the cost of a full internal team.

How long does it take to build a GRC program?

That depends on where you're starting from and which frameworks you need to meet. A focused compliance program for a single framework (like CMMC or SOC 2) might take 6–10 weeks to build and document. A broader enterprise GRC program can take 3–6 months. We establish a timeline during the discovery phase so you know what to expect before we start.

We already have some policies in place. Do you start from scratch?

No — we start with a gap assessment of what you already have. Many organizations have policies that are partially complete, outdated, or not aligned to the frameworks their auditors expect. We identify what's usable, what needs updating, and what's missing. You keep what works.

Can you help us prepare for a specific audit or certification, like CMMC or SOC 2?

Yes. Audit preparation is one of our most common engagements. We run a gap assessment against the specific framework, help you remediate gaps, organize evidence, and walk your team through what to expect. Cyberix itself holds CMMC Level 2, SOC 2 Type II, and ISO/IEC 27001, so we know exactly what these processes require from the inside.

Do you only work with large enterprises?

No. A significant part of our client base is small-to-mid-sized businesses and government contractors who need enterprise-grade GRC expertise without the budget for a full internal team. We scale our services to match your size and needs.

What happens after the initial program is built?

Regulations change, your business changes, and new risks emerge. We offer ongoing GRC management to keep your program current, monitoring your compliance posture, updating controls as needed, running periodic risk reviews, and producing regular reports for leadership and auditors. Think of us as an extension of your team, not a one-time project.

Don't Wait for the Audit Notice

Build a compliance program you can actually rely on

Legal and compliance leaders now rate business risk at 7.9 out of 10, and technology risk is the top concern. Organizations
that treat governance, risk, and compliance as separate functions spend more, get less, and are always reacting. Let's fix that.

Get a Free Assessment